HIPAA sets privacy and security obligations in the United States for covered entities and business associates. Its applicability depends on the organization, the service and the use.
Laura MéndezIllustrative patient record
Reception
Identity and schedulingPACS restricted
Clinical
Records and PACSAccess for the assigned role
Laura’s story · Illustrative example
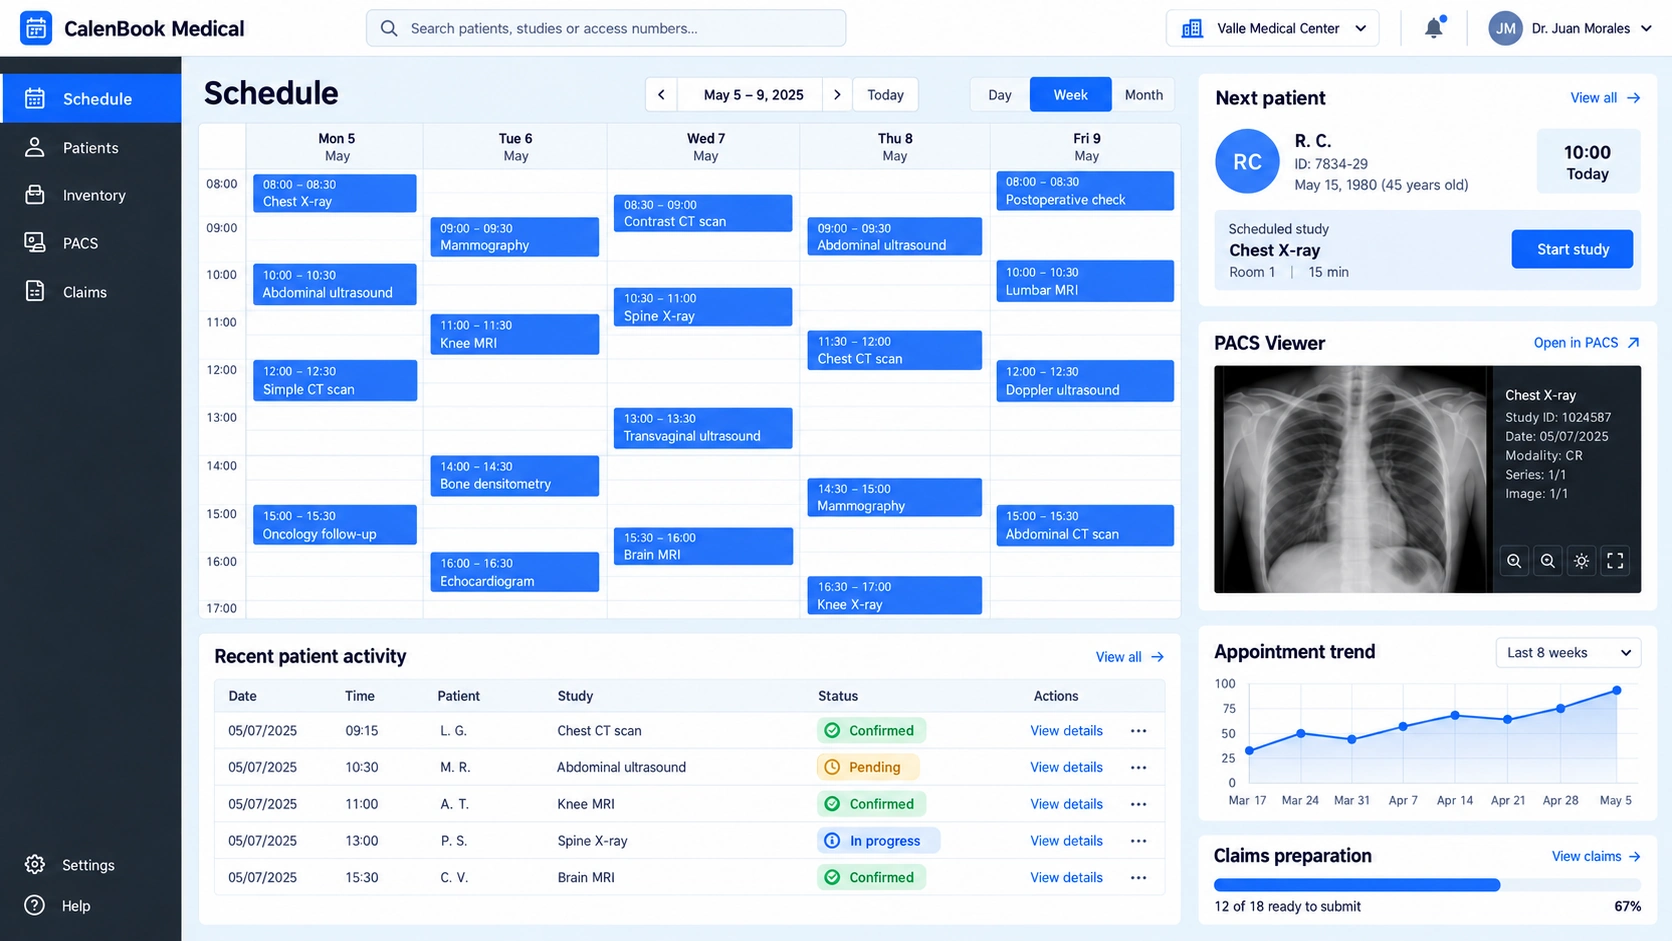
Reception confirms Laura’s appointment. The clinical team views the study according to their responsibilities and permissions.
Purposeful access, clear policies and safeguards.
US law · Applicability by organization and service
SOC 2 allows a service organization’s controls to be examined independently within a defined scope. We are preparing documentation and evidence for that process.
From intention to evidence
PoliciesDefine responsibilities
01
ControlsDocument how we operate
02
EvidencePrepare for assessment
03
Laura’s story · Illustrative example
The clinic needs to assess how access is reviewed: the policy, control and evidence need to connect.
Documented controls. Preparation for an independent examination.
ISO/IEC 27001 defines requirements for an information security management system: assess risks, assign responsibilities and review controls. Our preparation aims to sustain that continual improvement.
Risk management
01Assess
02Protect
03Review
04Improve
Laura’s story · Illustrative example
The clinic grows and adds a location. Access and risks change; the assessment needs to be updated.
A management system with defined risks and responsibilities.
In preparation · No CalenBook ISO/IEC 27001 certification
COBIT offers a framework for technology governance and management, connecting business objectives, responsibilities and decisions. We use it as a reference for that direction.
Business objective01
Decisions02
Owners03
Review04
Laura’s story · Illustrative example
Continuity of care is the priority. Leadership sets the goal; accountable owners coordinate execution and oversight.
Clear goals. Defined responsibilities. Decisions with direction.
Reference framework · Technology governance and management